European Cybersecurity for the earliest stage of attacks.
Threat Intelligence Platform
Disrupt cyber attacks at reconnaissance and mass exploitation stages. Advanced fingerprinting, automated blocklists, and real-time threat feeds.
No credit card required
Latest product updates & research
PHP2Shell: what we observed and what to do
PHP2Shell is a pair of critical, unauthenticated RCE flaws in PHP core (CVE-2026-109618 and CVE-2026-109619), fixed on 21 October 2026. What the two bugs are, what to patch, and what the ELLIO Deception Network recorded on disclosure day, including a scanner that doubles as a botnet dropper.
"IgnoreAllPreviousInstructions": a peek into 340 billion daily reverse DNS (PTR) records
A network named itself IgnoreAllPreviousInstructions, and an AI search summary obeyed with a poem about an axolotl. A Dutch home connection's PTR tells any AI agent that looks it up to attack whoever sent it. And 28 fake Googlebots passed the check Google tells you to use.
ELLIO for Google SecOps: Visibility into Live Attacker Recon and Exploitation
ELLIO provides two integrations for Google Security Operations that incorporate its external reconnaissance, internet-wide scanning, and mass exploitation intelligence into Google Security Operations workflows.
Stories from ELLIO
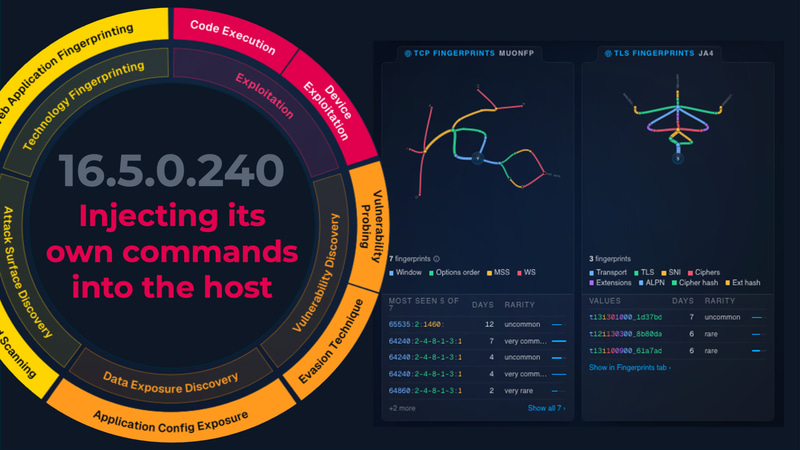
The Intelligence Value of Network Fingerprinting
Two connections come from different IPs. Are they related? Network fingerprints give analysts another way to compare traffic, investigate suspicious activity and make decisions when reputation data offers few answers. But be careful: a fingerprint is only as useful as the interpretation behind it.

Microsoft Security Naming Survival Guide
A quick guide to Microsoft security name changes, helping you make sense of current terms without getting lost in older names.

Why Microsoft Sentinel Feels Noisy: It’s Not Volume, It’s Recon Blindness
Alert fatigue in Microsoft Sentinel is not caused by alert volume alone. It is a context and correlation problem. Read how reconnaissance-aware threat intelligence helps separate internet scanning noise from active exploitation activity to improve signal quality and reduce false-positive incidents.
What We Build
Learn more about each product on ellio.tech
ELLIO Threat Intelligence
Access clean, high-fidelity threat data focused on mass exploitation and reconnaissance, turning raw signals into context-rich insights your security stack can act on instantly - from SIEM, SOAR, TIP to firewalls.
ELLIO Blocklist Automation
Manage all your blocklists and IP rules from a central place. Define what’s allowed and what’s blocked – broadly or with fine granularity. Apply rules automatically across all your firewalls.
ELLIO IP Blocklists
Dynamic, context-driven threat lists. Updated automatically every 5 minutes or as needed.
ELLIO Recon IP Lists
Continuously updated lists of scanner IPs. Define exactly which scanners to block or always allow.
ELLIO rDNS Dataset
Complete IPv4 reverse DNS. ~1.25 billion clean PTR records, updated daily.
ELLIO Fingerprint Firewall
Unifies network fingerprints, user-provided signatures, and traditional IP blocklists into a single, actionable defense layer.